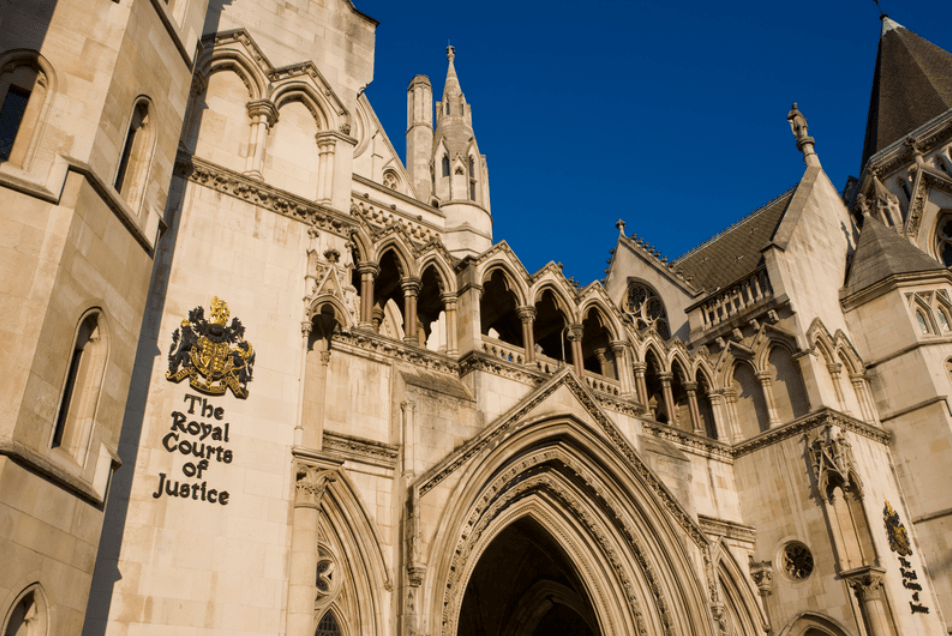
On 22 August 2025, the Courtroom of Attraction handed down a landmark judgment in Farley & Ors v Paymaster (1836) Restricted (buying and selling as Equiniti). The case involved a large-scale information breach wherein over 750 annual pension profit statements of Sussex Cops have been mistakenly despatched to outdated addresses. Greater than 450 officers introduced claims beneath the GDPR and Information Safety Act 2018, alleging misery, worry of misuse, and in some circumstances psychiatric harm.
The Excessive Courtroom had beforehand struck out most claims, holding that compensation was solely accessible if the claimants may present that their information was truly accessed by unauthorised third events, and that claims beneath a “threshold of seriousness” weren’t legally viable. Solely 14 claims survived.
The Courtroom of Attraction has now overturned that place, in a judgment with vital penalties for information safety litigation and organisational legal responsibility within the UK.
For organisations, the message is obvious: even minor errors in dealing with private information can now result in legal responsibility. The ruling will possible gas an increase in collective actions and reshape the litigation panorama for information safety within the UK. Companies should deal with information accuracy and safety not simply as compliance obligations, however as core danger administration priorities.
Key findings by the Courtroom of Attraction
Illegal “processing” is sufficient — disclosure isn’t required
The Excessive Courtroom handled disclosure to a 3rd get together as a crucial situation for an information safety declare. The Courtroom of Attraction disagreed, holding that “processing” beneath the GDPR is outlined broadly and contains storing, altering, and sending information to the unsuitable handle . Whether or not or not a 3rd get together truly opened the envelope was irrelevant, the illegal processing itself was a breach.
This aligns UK legislation extra carefully with the CJEU’s interpretation of “processing”, which stresses its broad scope and doesn’t require disclosure to finish the unsuitable.
There isn’t any “threshold of seriousness” beneath GDPR
The Courtroom of Attraction dominated that there isn’t any minimal degree of hurt that should be crossed earlier than compensation may be awarded. The Excessive Courtroom’s reliance on the “threshold of seriousness” take a look at (drawn from Lloyd v Google) was misplaced.
As a substitute, the Courtroom of Attraction adopted latest CJEU selections (Austria Put up, VB v Bulgarian Income Company, BL v MediaMarkt) which held that Article 82 GDPR precludes home courts from imposing such a threshold. A claimant should present precise harm, however that harm doesn’t must be “severe” to be compensable.
This additionally aligns with a case from Germany in 2024, {that a} mere lack of management over private information can represent non-material harm beneath Article 82 of GDPR.
Compensation for “worry of misuse” is feasible
The Courtroom held that worry of misuse of non-public information can qualify as “non-material harm”, supplied that worry is objectively well-founded. This expands the recognised scope of compensable harms past misery alone.
For instance, cops who feared that criminals would possibly entry delicate pension and employment particulars may declare compensation, even when there was no proof that the envelopes had been opened .
Low-value claims aren’t inherently abusive
The Excessive Courtroom had dismissed giant numbers of claims as abusive as a result of their worth was too low. The Courtroom of Attraction firmly rejected this, holding that modest claims must be managed proportionately (e.g., small claims monitor allocation) fairly than struck out wholesale. Abuse should be assessed individually, not in bulk.
Why this ruling issues for UK information safety
Stronger rights for claimants
This resolution lowers the bar for information breach victims. Claimants not have to show precise entry by unauthorised events, nor that their misery crosses a judicially imposed “seriousness” threshold. Concern of misuse, if real and cheap, is compensable. This makes claims extra accessible, significantly in large-scale breaches the place proof of entry is commonly unimaginable.
Elevated legal responsibility for organisations
Information controllers and processors now face better litigation publicity. Even technical errors like outdated addresses or system flaws might result in compensable hurt. Organisations can’t depend on the argument that “nobody truly noticed the info” as a defence.
Corporations should subsequently strengthen information accuracy, system integrity, and breach response protocols, as even low-level errors might result in legal responsibility.
Rigidity with Lloyd v Google
The ruling creates obvious friction with the Supreme Courtroom’s 2021 resolution in Lloyd v Google, which had emphasised seriousness and rejected “lack of management” damages. The Courtroom of Attraction distinguished Lloyd as being concerning the Information Safety Act 1998 and consultant actions, however the rigidity stays. Until the Supreme Courtroom revisits the difficulty, uncertainty may persist.
Case administration pressures
The judgment recognises the chance of courts being flooded with low-value claims however insists that proportionality must be managed procedurally, not by hanging out claims in bulk. This may possible speed up the pattern in direction of information breach group claims and lift questions on how courts deal with tons of or 1000’s of modest claims.
Sensible takeaways for organisations following Farley
Assessment handle and make contact with information integrity: As seen on this case, technical database errors can create vital legal responsibility. Common audits and updates are important.
Improve breach notification protocols: Concern of misuse should be “objectively well-founded” which means poor communication or obscure reassurances can worsen organisational publicity.
Count on extra claims: Legislation corporations could also be emboldened to carry mass actions for even minor breaches. Insurers and in-house authorized groups ought to reassess publicity.
Don’t dismiss low-value incidents: Even when particular person claims are price £250–£1,000, collective actions can escalate prices and reputational dangers dramatically.
On 22 August 2025, the Courtroom of Attraction handed down a landmark judgment in Farley & Ors v Paymaster (1836) Restricted (buying and selling as Equiniti). The case involved a large-scale information breach wherein over 750 annual pension profit statements of Sussex Cops have been mistakenly despatched to outdated addresses. Greater than 450 officers introduced claims beneath the GDPR and Information Safety Act 2018, alleging misery, worry of misuse, and in some circumstances psychiatric harm.
The Excessive Courtroom had beforehand struck out most claims, holding that compensation was solely accessible if the claimants may present that their information was truly accessed by unauthorised third events, and that claims beneath a “threshold of seriousness” weren’t legally viable. Solely 14 claims survived.
The Courtroom of Attraction has now overturned that place, in a judgment with vital penalties for information safety litigation and organisational legal responsibility within the UK.
For organisations, the message is obvious: even minor errors in dealing with private information can now result in legal responsibility. The ruling will possible gas an increase in collective actions and reshape the litigation panorama for information safety within the UK. Companies should deal with information accuracy and safety not simply as compliance obligations, however as core danger administration priorities.
Key findings by the Courtroom of Attraction
Illegal “processing” is sufficient — disclosure isn’t required
The Excessive Courtroom handled disclosure to a 3rd get together as a crucial situation for an information safety declare. The Courtroom of Attraction disagreed, holding that “processing” beneath the GDPR is outlined broadly and contains storing, altering, and sending information to the unsuitable handle . Whether or not or not a 3rd get together truly opened the envelope was irrelevant, the illegal processing itself was a breach.
This aligns UK legislation extra carefully with the CJEU’s interpretation of “processing”, which stresses its broad scope and doesn’t require disclosure to finish the unsuitable.
There isn’t any “threshold of seriousness” beneath GDPR
The Courtroom of Attraction dominated that there isn’t any minimal degree of hurt that should be crossed earlier than compensation may be awarded. The Excessive Courtroom’s reliance on the “threshold of seriousness” take a look at (drawn from Lloyd v Google) was misplaced.
As a substitute, the Courtroom of Attraction adopted latest CJEU selections (Austria Put up, VB v Bulgarian Income Company, BL v MediaMarkt) which held that Article 82 GDPR precludes home courts from imposing such a threshold. A claimant should present precise harm, however that harm doesn’t must be “severe” to be compensable.
This additionally aligns with a case from Germany in 2024, {that a} mere lack of management over private information can represent non-material harm beneath Article 82 of GDPR.
Compensation for “worry of misuse” is feasible
The Courtroom held that worry of misuse of non-public information can qualify as “non-material harm”, supplied that worry is objectively well-founded. This expands the recognised scope of compensable harms past misery alone.
For instance, cops who feared that criminals would possibly entry delicate pension and employment particulars may declare compensation, even when there was no proof that the envelopes had been opened .
Low-value claims aren’t inherently abusive
The Excessive Courtroom had dismissed giant numbers of claims as abusive as a result of their worth was too low. The Courtroom of Attraction firmly rejected this, holding that modest claims must be managed proportionately (e.g., small claims monitor allocation) fairly than struck out wholesale. Abuse should be assessed individually, not in bulk.
Why this ruling issues for UK information safety
Stronger rights for claimants
This resolution lowers the bar for information breach victims. Claimants not have to show precise entry by unauthorised events, nor that their misery crosses a judicially imposed “seriousness” threshold. Concern of misuse, if real and cheap, is compensable. This makes claims extra accessible, significantly in large-scale breaches the place proof of entry is commonly unimaginable.
Elevated legal responsibility for organisations
Information controllers and processors now face better litigation publicity. Even technical errors like outdated addresses or system flaws might result in compensable hurt. Organisations can’t depend on the argument that “nobody truly noticed the info” as a defence.
Corporations should subsequently strengthen information accuracy, system integrity, and breach response protocols, as even low-level errors might result in legal responsibility.
Rigidity with Lloyd v Google
The ruling creates obvious friction with the Supreme Courtroom’s 2021 resolution in Lloyd v Google, which had emphasised seriousness and rejected “lack of management” damages. The Courtroom of Attraction distinguished Lloyd as being concerning the Information Safety Act 1998 and consultant actions, however the rigidity stays. Until the Supreme Courtroom revisits the difficulty, uncertainty may persist.
Case administration pressures
The judgment recognises the chance of courts being flooded with low-value claims however insists that proportionality must be managed procedurally, not by hanging out claims in bulk. This may possible speed up the pattern in direction of information breach group claims and lift questions on how courts deal with tons of or 1000’s of modest claims.
Sensible takeaways for organisations following Farley
Assessment handle and make contact with information integrity: As seen on this case, technical database errors can create vital legal responsibility. Common audits and updates are important.
Improve breach notification protocols: Concern of misuse should be “objectively well-founded” which means poor communication or obscure reassurances can worsen organisational publicity.
Count on extra claims: Legislation corporations could also be emboldened to carry mass actions for even minor breaches. Insurers and in-house authorized groups ought to reassess publicity.
Don’t dismiss low-value incidents: Even when particular person claims are price £250–£1,000, collective actions can escalate prices and reputational dangers dramatically.